
Apple wants you to believe it can process your camera and microphone data without ever seeing it. That’s a bold promise, and it’s worth reading closely before you accept it.
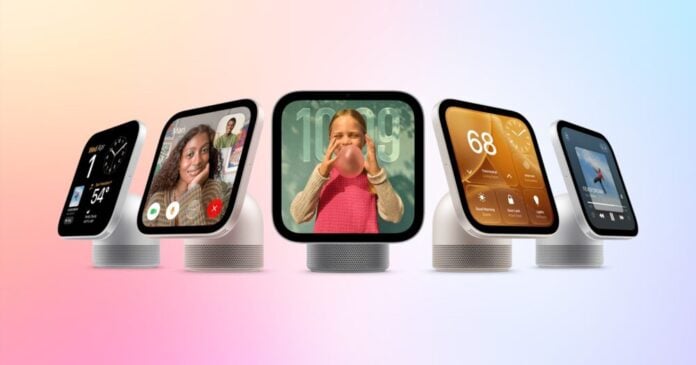
Apple shared a detailed look at Secure Exclaves, which it uses to protect camera and microphone data on the HomeView, the iPhone 18 Pro, and other products. The company describes them as compartmentalized runtimes that handle sensor data in isolation from the rest of the operating system. According to Apple, data processed inside an exclave is not available to the OS, to apps, or to Apple. And it can still use the full application processor.
That last part matters. Earlier secure designs, like dedicated enclaves on separate silicon, traded away performance for isolation. Running on the main processor means face recognition, speech handling, and scene analysis can happen on-device with real horsepower. That reduces the argument for shipping raw audio and video to a server. For an always-listening, always-watching home device, that’s the right direction.
But we should be precise about what is actually promised. Isolation from apps and the OS is a meaningful reduction in attack surface. A compromised app, or even a kernel bug, shouldn’t be able to scrape a live camera feed. That’s a real gain, given how often spyware has abused camera and mic access.
The phrase “not available to Apple” is the harder claim. It describes a design intent, not something you can verify yourself. Who writes the code running inside the exclave? Apple. Who signs it and ships updates? Apple. An isolated runtime protects data from everything outside it, but you still trust whatever runs inside. Apple’s own history with on-device scanning proposals shows that policies can change even when architecture stays put.
Then there’s output. Exclaves protect raw sensor data, but whatever they emit, such as a detected person, a transcribed command, or a motion alert, leaves the box. What gets sent, where, and how long it’s kept is the privacy question that matters most, and isolation alone doesn’t answer it.
The bigger picture is a trend. Apple, Google, and Microsoft are all moving sensitive processing into hardware-backed compartments, partly because on-device AI needs constant access to cameras and microphones. The pitch is that more intelligence can coexist with more privacy. Sometimes that’s true.
So what should users and researchers want? Independent audits of the exclave code paths. Clear documentation of every data flow leaving the isolated runtime. Hardware indicators that can’t be bypassed. And a bug bounty that treats exclave escapes as top-tier findings.
Secure Exclaves look like a solid engineering step. Treat them as a promising claim, not a proven guarantee, until outsiders have had a chance to break them.